BIND
BIND is a collection of tools for the DNS ecosystem.
For example, BIND includes named, a popular authoritative DNS server and recursive resolver,
and dig, a common resolver client for DNS lookups.
BIND can integrate with HSMs via the PKCS#11 API, facilitated through OpenSSL. This allows BIND to delegate key generation and signing to an HSM. Through this integration you can keep your DNSSEC signing keys securely in a tamper-proof, high-performance HSM. This allows for professional key management throughout the key lifecycle, including key generation, backup, and rollover.
For an introduction to how DNSSEC works, including how zones are signed and the roles of Zone Signing Keys (ZSK) and Key Signing Keys (KSK), see this article from Cloudflare.
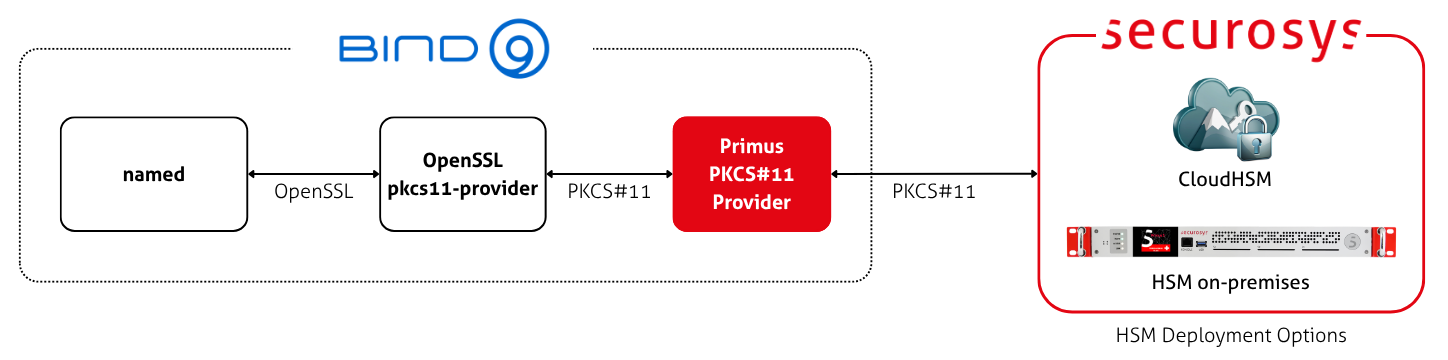
Benefits
- Secure your DNS: Sign your DNS zone with DNSSEC for integrity and authentication.
- Secure your keys: Keep your DNSSEC signing keys securely inside a Primus HSM.
- High availability: Deploy your Primus HSMs as an auto-syncing, geo-redundant cluster.
- High performance:
- A single Primus HSM can deliver thousands of EC key generations per second and tens of thousands of EC signatures per second. Performance scales linearly with the number of devices in a cluster.
- Key generation is required during ZSK and KSK rollovers. Signing is required whenever the zone changes, such as when records are added or updated.
Get Started
Follow the installation guide to learn how to set up BIND together with Primus HSM.